Checkmarx earns FedRAMP Moderate certification for government AppSec platform
By SSN Staff
Updated 11:59 AM CDT, Tue July 14, 2026
PARAMUS, N.J.—Checkmarx announced that its Checkmarx One for Government application security platform has achieved FedRAMP Moderate certification and is now listed in the FedRAMP Marketplace, allowing federal agencies to more easily procure and deploy the platform.
According to the company, the certification comes as federal agencies seek tools to secure increasingly complex software development environments while complying with government cybersecurity requirements.
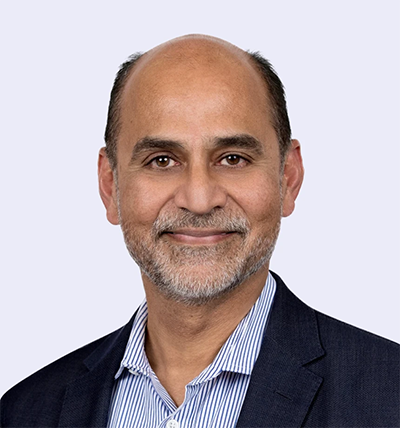 “In an AI-driven world where the velocity of software development is accelerating and the threat landscape is multiplying even faster, application security has never been more critical,” said Sandeep Johri, CEO of Checkmarx. “Federal agencies making long-term security investments need a platform that provides visibility, governance and risk-based prioritization across the entire software lifecycle.”
Checkmarx said more than 100 government agencies already use its technology. Kevin Hayes, senior director of public sector sales, said the certification process provided insight into the challenges facing federal development and security teams.
“This process gave us direct insight into the challenges federal development and security teams specifically face, including fragmented security tooling, accelerating software delivery cycles, and increasingly complex compliance requirements,” Hayes said. “Checkmarx One for Government was built to help agencies address those challenges with comprehensive testing and centralized risk management.”
FedRAMP Moderate certification enables federal agencies to adopt the platform through a streamlined security review and procurement process. Checkmarx noted that the Moderate baseline supports most civilian agency workloads while additional deployment options are available for organizations with more stringent security requirements.
Checkmarx One for Government combines multiple application security capabilities within a single platform, including static application security testing (SAST), software composition analysis (SCA), malicious package detection, infrastructure-as-code security, container security and application security posture management (ASPM).
The company said its ASPM capability provides a consolidated view of application risk across source code, open-source dependencies, infrastructure, containers and cloud environments. By correlating findings across security domains, the platform is designed to help organizations prioritize vulnerabilities, reduce remediation times and maintain compliance throughout the software development lifecycle.

Comments